Spyware Rode the Ad Auction: How 'AdFection' Put Candiru Code on Al Jazeera Devices
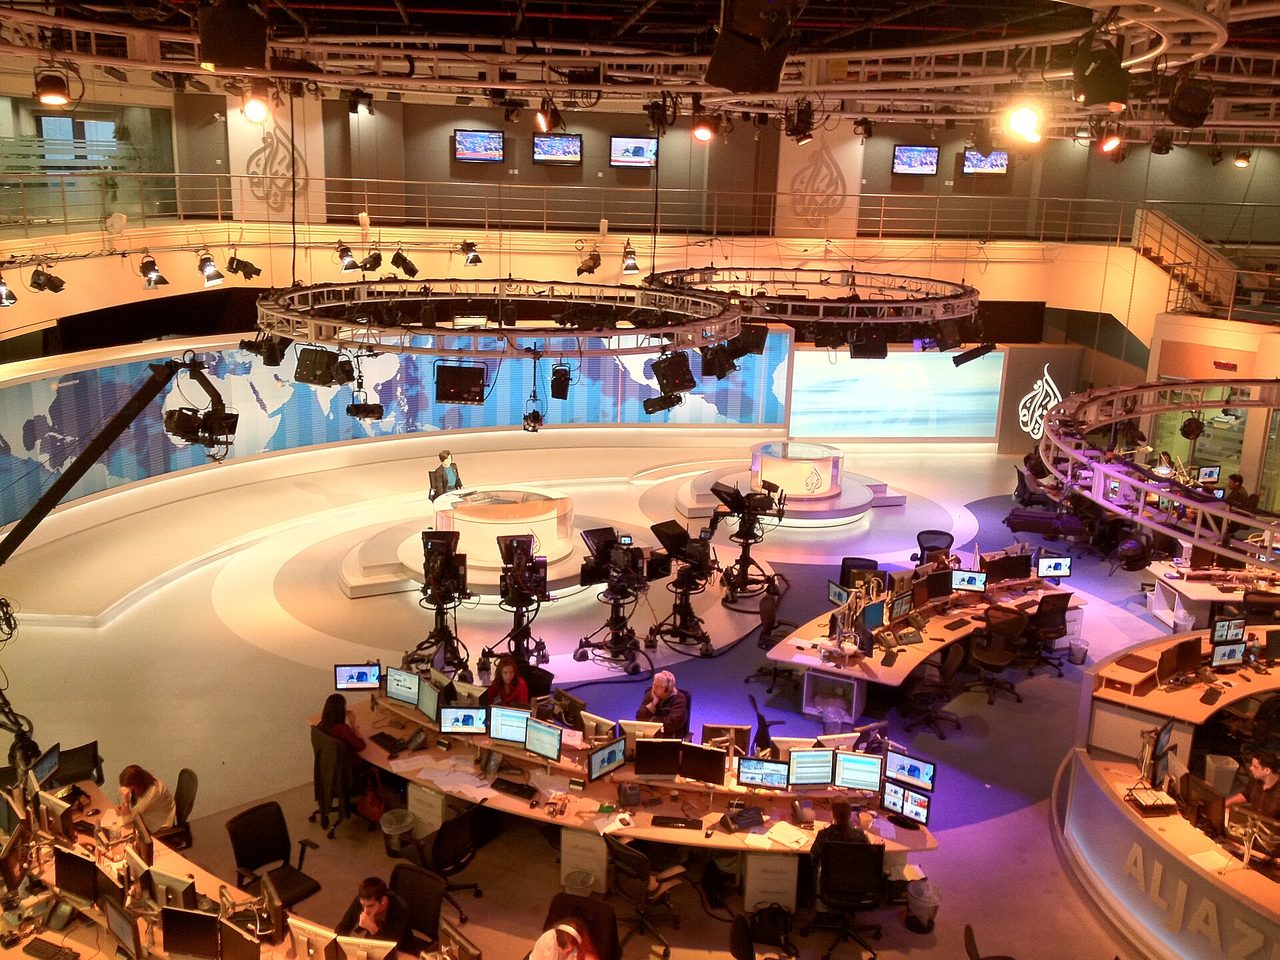
Photo: Wittylama / CC BY-SA 3.0 · via Wikimedia Commons
Spyware Rode the Ad Auction: How 'AdFection' Put Candiru Code on Al Jazeera Devices
No Click, No Warning, Not Even an Ad in Sight
The Citizen Lab at the University of Toronto published its 195th report, "Exposing AdFection," on October 15, offering what its authors call the first public technical confirmation that mercenary spyware can reach a real device through ordinary targeted advertising. No click, no download, no link, no visible sign anything happened. The researchers named the technique AdFection. "Someone who gets hacked like this would not see anything amiss," senior researcher Bill Marczak told WIRED. "In fact, they might not even see any ad at all."
A Bidder Built for Targeting, Not for Selling
The company at the centre of the report is Discover-Tech, an Israeli digital advertising agency founded in 2020 that presents itself as a specialist ad firm. Citizen Lab describes it instead as a "bridge between ad vendors and the mercenary spyware ecosystem." Its platform, Controlium, let customers upload target lists — mobile advertising IDs, Beeswax or MyDSP cookie IDs, IP addresses — pick a payload type flagged "de-anon," restrict a campaign by country, and keep bidding until the ad landed on the chosen device.
45 Al Jazeera Devices Confirmed
The confirmed victims worked at Al Jazeera. Between 2024 and 2025, at least 45 devices at the Qatari broadcaster were targeted after being served ads, and Citizen Lab linked the infections to spyware from Candiru with high confidence. The investigation only became possible because the network handed its own logs to the researchers. Those logs show the same sequence each time: an ad impression from Discover-Tech infrastructure, a Candiru validator check within seconds, an exploit server, then command-and-control traffic within one to three minutes.
The Ads Reached Military and Nuclear Networks
The blast radius went far beyond one newsroom. According to the report as covered by Ars Technica, Discover-Tech impressions appeared on networks belonging to NATO, the United Nations, European Union legislative bodies, Australian critical infrastructure, and armed forces and government agencies in Norway and Sweden. Confiant, the New York ad-security firm that investigated alongside Citizen Lab, said some impressions also landed on sensitive networks used by the Pentagon, the International Atomic Energy Agency and the International Criminal Court.
Government Networks in at Least 24 Countries
Al Jazeera reported on October 16 that government networks were hit in at least 24 countries, among them the United States, Italy, Denmark, Norway, Australia, Russia, Mexico and Israel itself. Media organisations were targeted mainly in Australia, Denmark and Sweden. Researchers also found signs of potentially malicious ads aimed at journalists at up to 18 other news outlets.
Google and IAB Europe Cut Ties
The platforms moved quickly once told. Google said that after a joint investigation with Citizen Lab and Confiant it blocked Discover-Tech from its ad platforms for "systematically violating our policies," and added Safe Browsing warnings for linked sites. IAB Europe suspended the company from its Global Vendor List after an audit, saying confirmed spyware findings could justify permanent expulsion. Beeswax, Vungle (Liftoff) and Eskimi also removed or paused it. Neither Discover-Tech nor Candiru answered Citizen Lab's questions, and Reuters could not reach Discover-Tech chief executive Dekel Boni.
The Spyware Behind It Was Sanctioned in 2021
Candiru, an Israeli spyware vendor, was added to the US Commerce Department's Entity List in 2021 over allegations it supplied technology used against government officials, journalists, activists and academics. The report says the company has since been acquired and rebranded as Integrity Labs. It is not Candiru's first run at Al Jazeera: in 2020, Citizen Lab found that Pegasus spyware from NSO Group had infected the phones of 36 of the network's journalists, producers, anchors and executives.
Zero-Byte Replies Kept Ad Scanners Blind
The design was built to slip past ad-industry checks. Scripts hidden in the creatives called back to Discover-Tech's NOAS servers, carrying the viewer's cookie ID or mobile advertising ID; only devices matching pre-set criteria received executable code, while everyone else got a zero-byte reply. That kept both the malicious payload and the pointers to it away from the ad vendors. Citizen Lab also found Controlium's authentication was broken: an unauthenticated download endpoint exposed 128 days of login logs covering 120 usernames, including accounts tied to surveillance vendors Candiru, Bindecy and Intelos.
A Second Actor Turned Ad IDs Into Phone Numbers
The report describes a separate threat actor it calls DARK CARTOGRAPHER, which used the same Discover-Tech infrastructure to exploit mobile carrier weaknesses and match device advertising IDs to real phone numbers across more than 30 countries — mass de-anonymisation of ordinary internet users. Citizen Lab says that actor's infrastructure links to both a mercenary adtech vendor and a US government contractor, that such MSISDN leaks have been exploited since at least 2019, and that a second report will follow.
Al Jazeera Wants Accountability; Researchers Want Regulators
Al Jazeera Media Network said it "condemns the targeting of devices belonging to several of its employees with spyware," called the targeting of journalists an assault on press freedom and the public's right to knowledge, and demanded that those responsible be held accountable. Citizen Lab aimed its criticism at the industry: the abuse ran for years and major ad vendors neither detected nor prevented it. "The way the online advertising ecosystem works today is a security threat for states, the private sector, civil society and everyone else alike," said researcher Wolfie Christl. The lab urged organisations to block ads at the network gateway and individuals to use ad blockers, reset or disable their mobile advertising ID, and keep software updated.
Sources
- Citizen Lab: Exposing AdFection: How Discover-Tech Turned Targeted Ads Into a Pipeline for Zero-Click Mercenary Spyware
- Confiant: ADINT: Weaponized Ad Tech for Zero-Click Spyware and Mass Identity Vacuuming
- Reuters: Israeli firm used online ads to run vast spy operation, researchers say
- Al Jazeera: How Israeli firm's 'zero-click' malware attack poses global security risk
- CPJ: Report: Israeli ad-tech firm enables spyware targeting of at least 45 Al Jazeera devices